
Audit your code locally via GitHub Actions. We never access your source code—your intellectual property stays 100% secure.
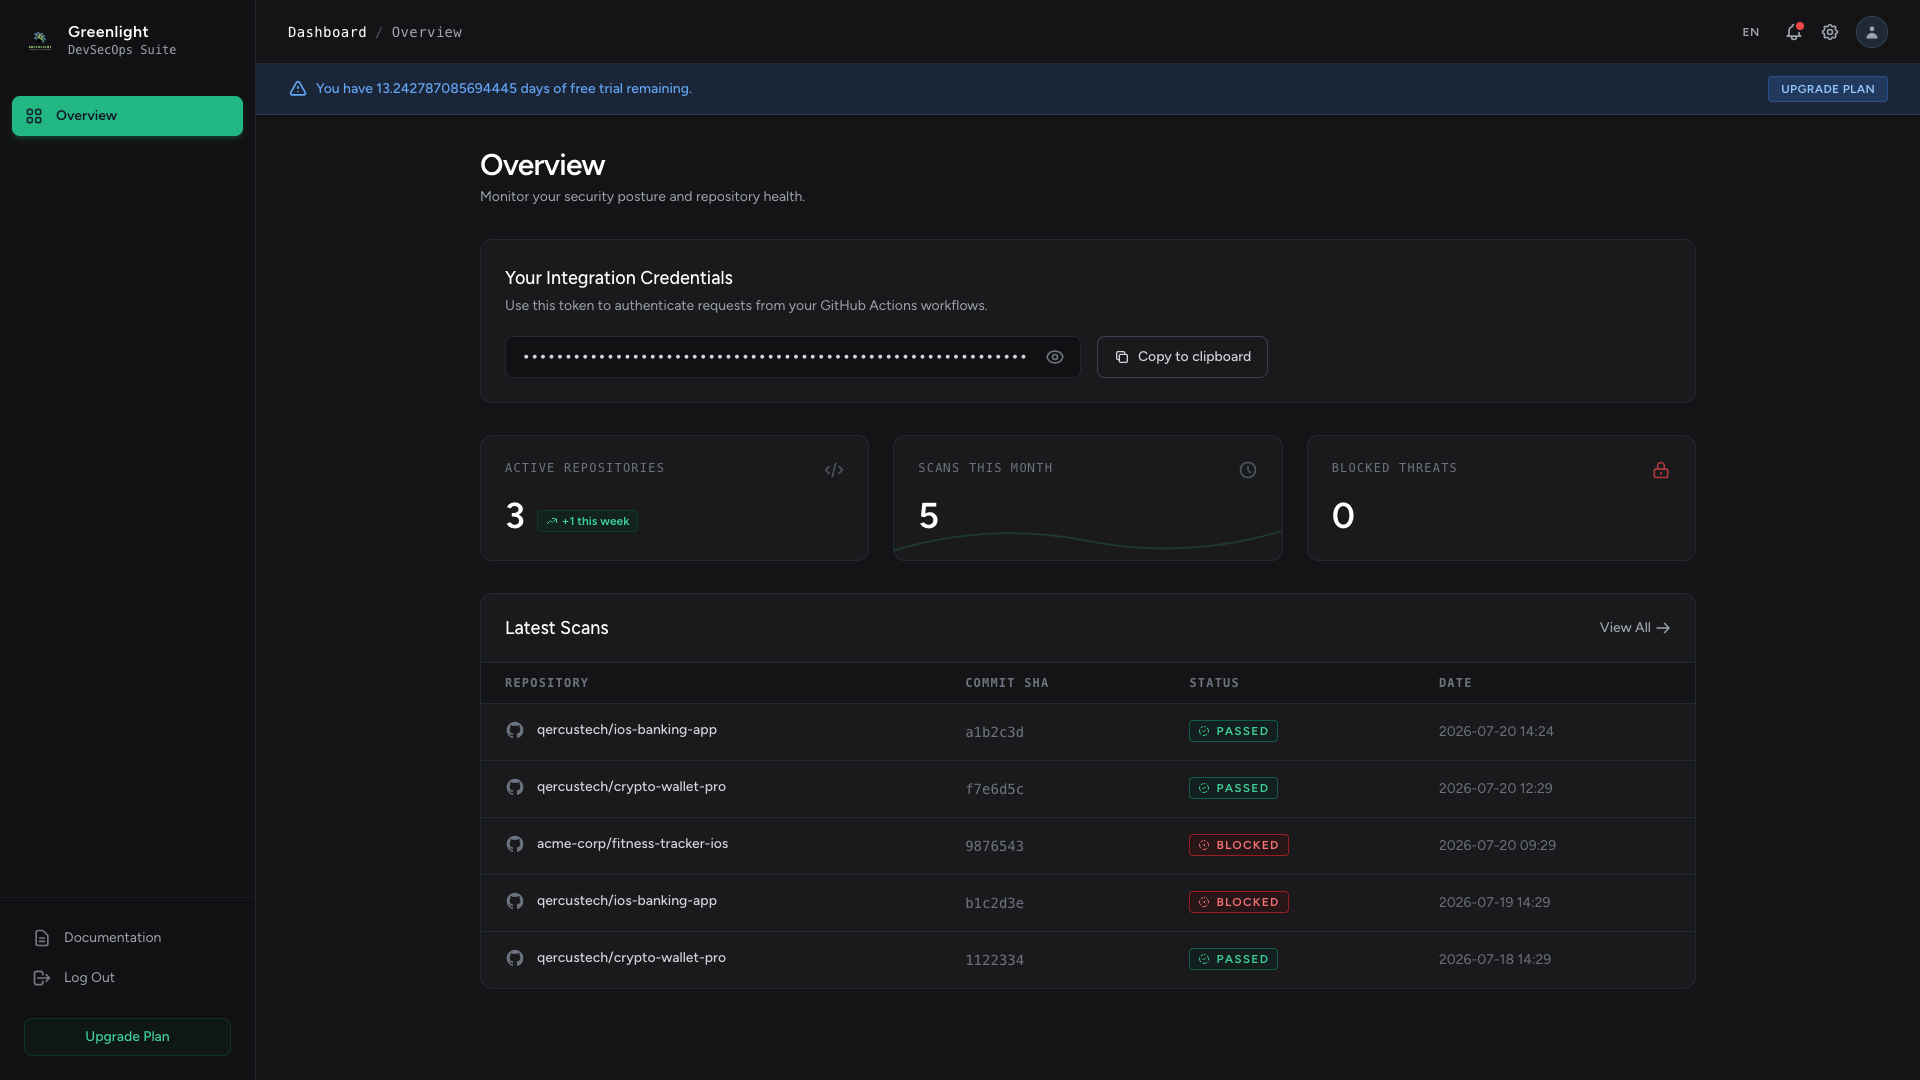
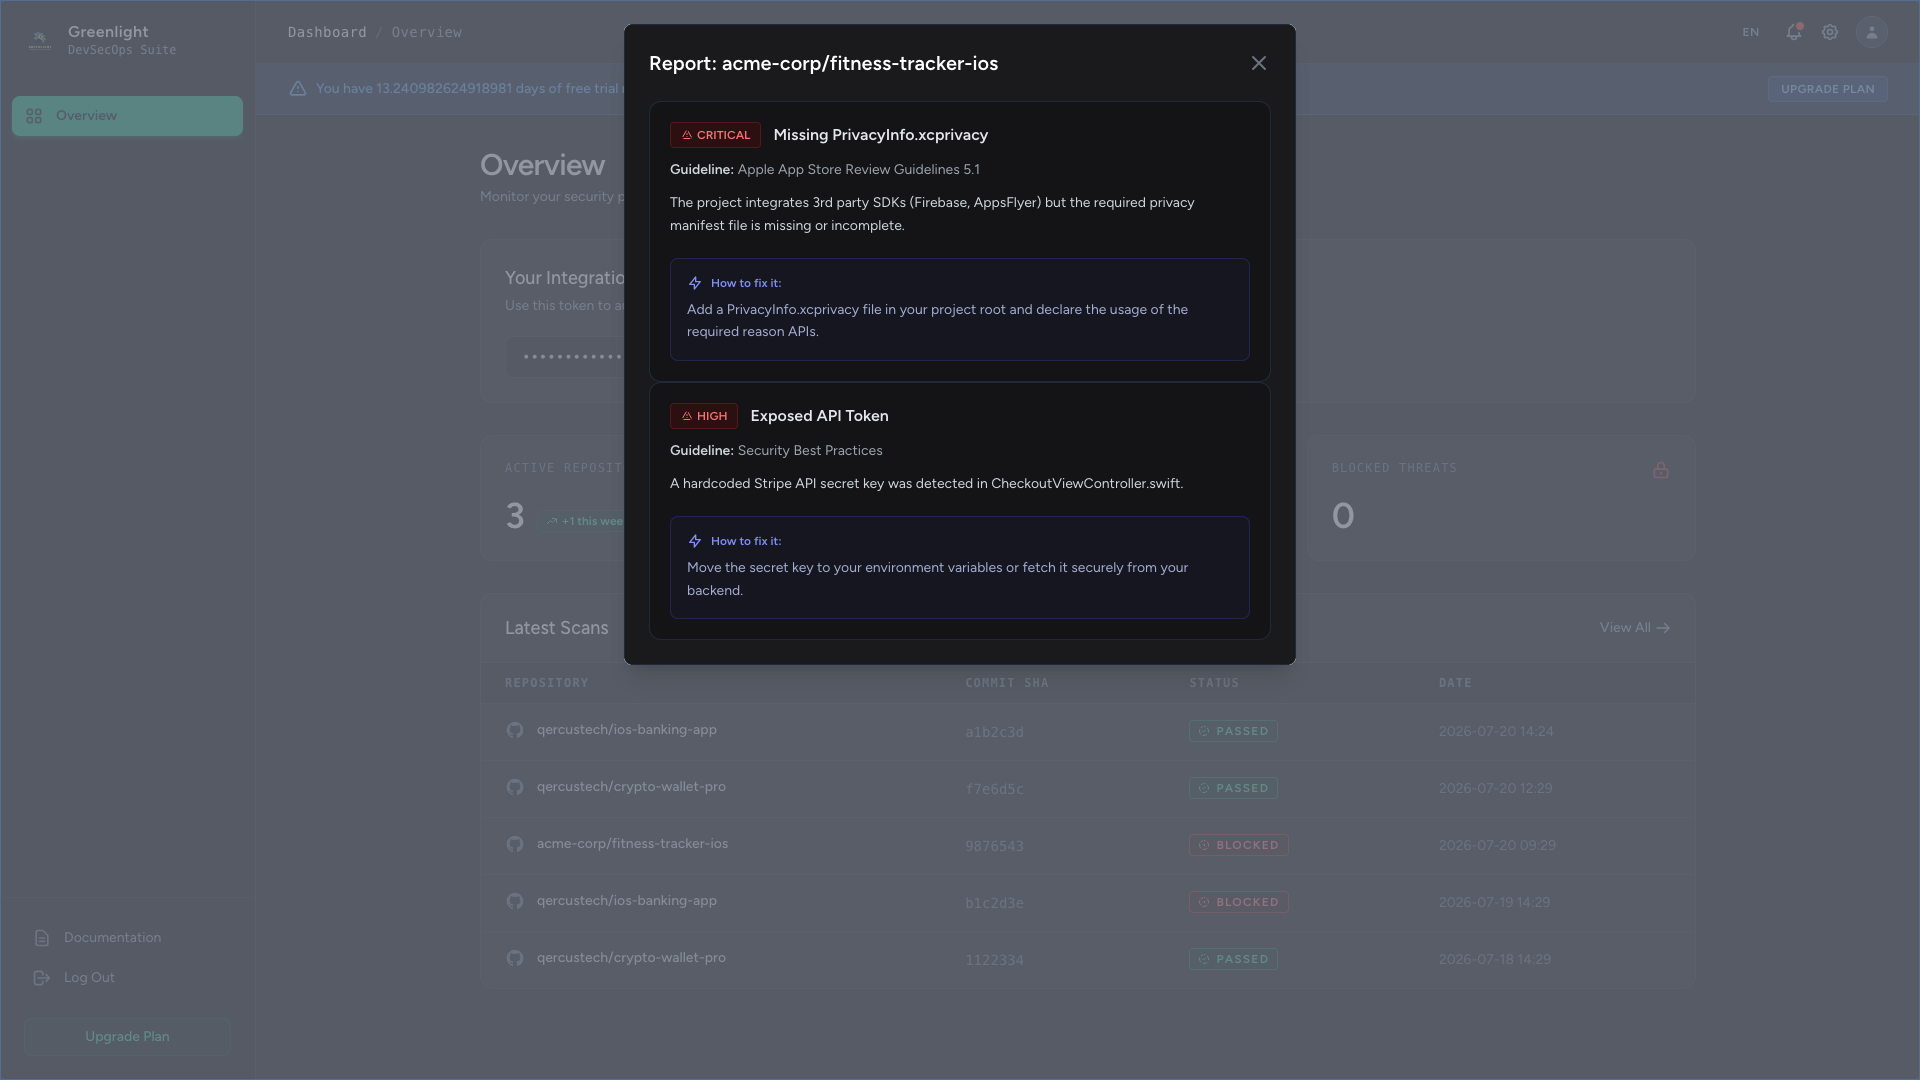
Our GitHub Action runs deep security analysis in fractions of a second without your code leaving your servers. Know exactly what we validate before Apple rejects your app.
Automated validation of app.json and Info.plist. We verify Bundle ID formatting, app names, versions, icon presence, privacy policy URLs, and Purpose Strings clarity.
Detection of over 30 critical risk patterns. We spot private API usage, exposed secrets and tokens, payment system violations, missing ATT (App Tracking Transparency) implementations, and incomplete "Sign in with Apple" integrations.
Strict validation of the PrivacyInfo.xcprivacy manifest. We cross-reference detected tracking SDKs and "Required Reason" APIs in your code against your official declarations to prevent technical rejections.
Verification of your final build structure. We check app size against Apple's cellular download limits, icon resolutions, launch storyboards, and third-party framework privacy manifests.
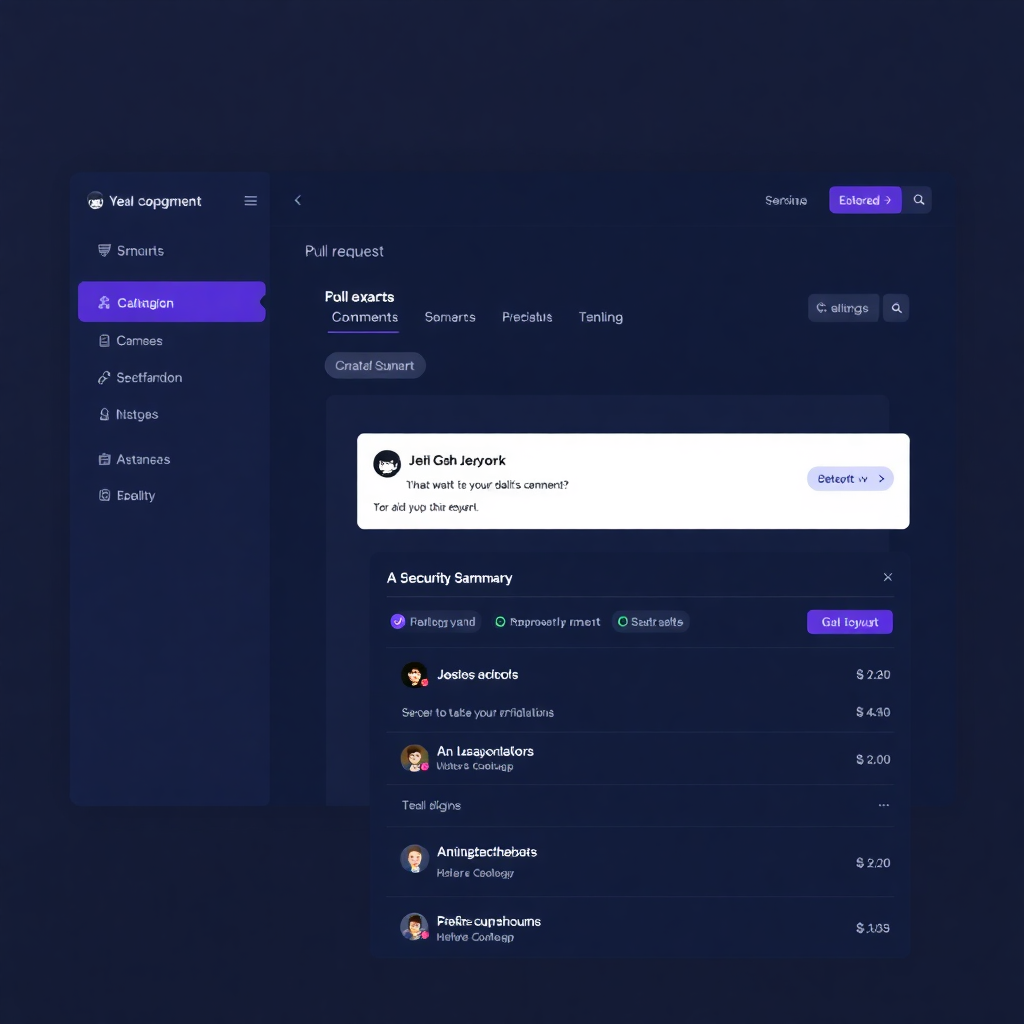
Security scan results delivered directly into your Pull Requests via automated comments and status checks.
Seguridad de nivel enterprise diseñada para equipos que no pueden permitirse riesgos.
Security analysis runs 100% inside your CI/CD pipeline. Your code never leaves your infrastructure.
Drop in our pre-configured GitHub Action in seconds. No complex setups or workflow delays.
Receive security scan results directly in your dashboard and Pull Requests with instant, actionable fixes.
Try all features free for 14 days. No credit card required.
We are accepting early testers. The Zero-Trust scanner is 100% free during this phase. No credit card required.
We are accepting early testers. The Zero-Trust scanner is 100% free during this phase. No credit card required.
We are accepting early testers. The Zero-Trust scanner is 100% free during this phase. No credit card required.